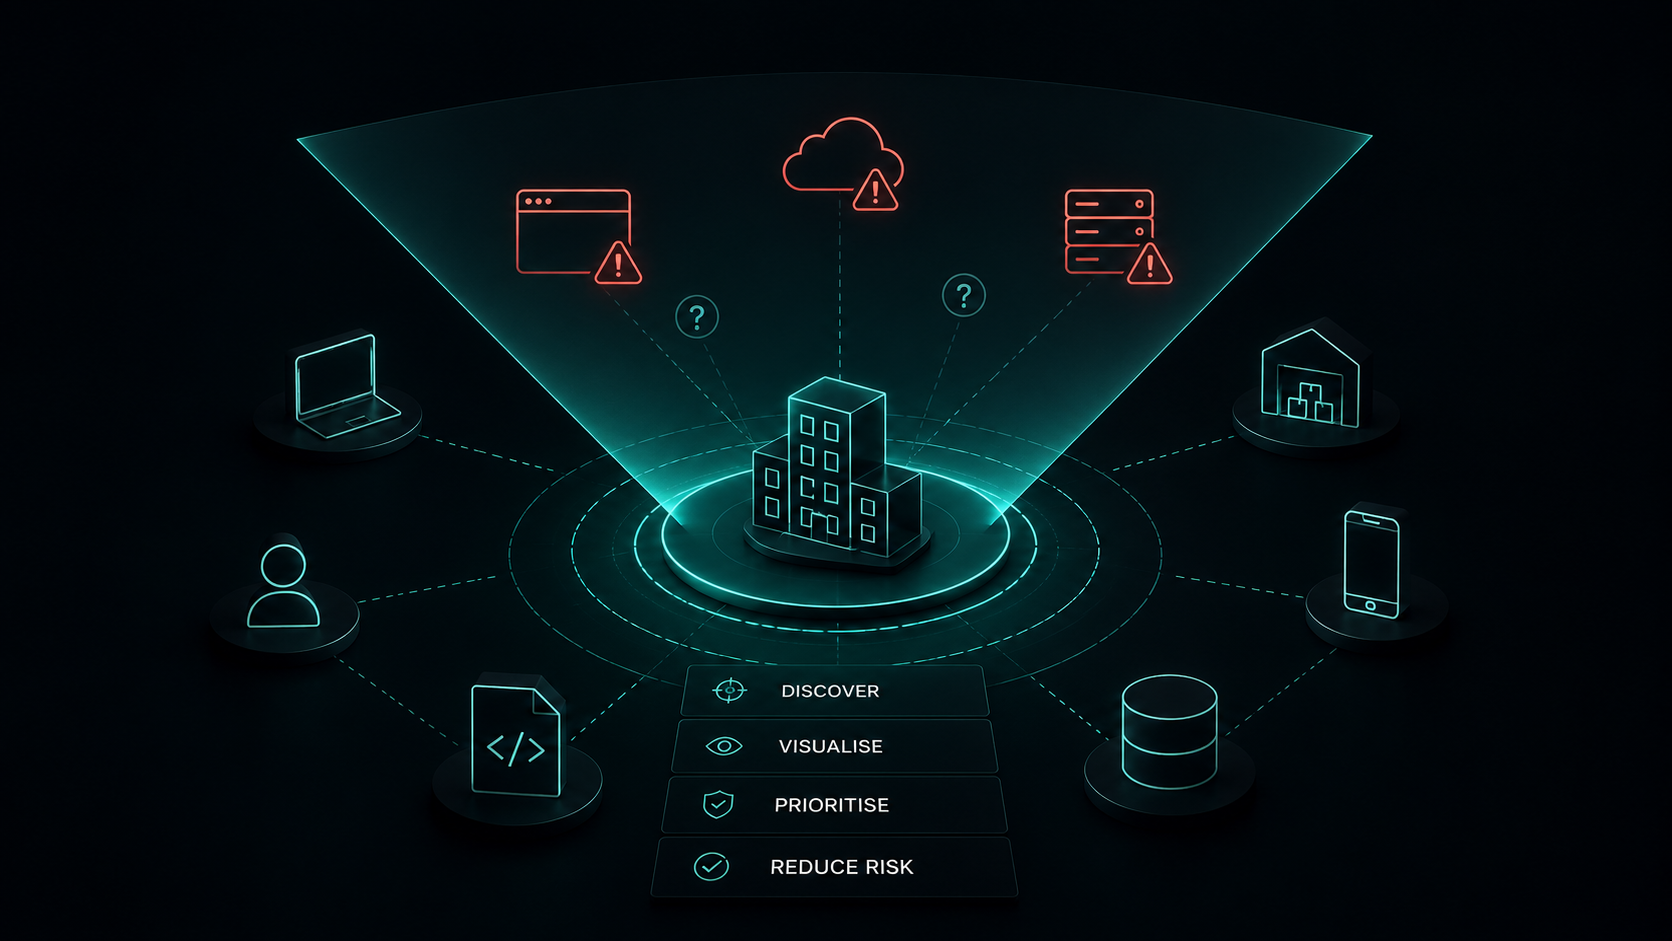
Almost 8000 organisations are already using Risk Ledger's cutting-edge platform for real-time supply chain security, which enables organisations to Defend-as-One because every link matters in cyber security.Visualising client-supplier networks, Risk Ledger is able to map interdependencies and risks well beyond organisations' immediate third-parties, into 4th, 5th and nth parties. This allows the uncovering of hidden concentration and systemic risks that could pose a threat to the cyber security and operational resilience of organisations and entire industries.
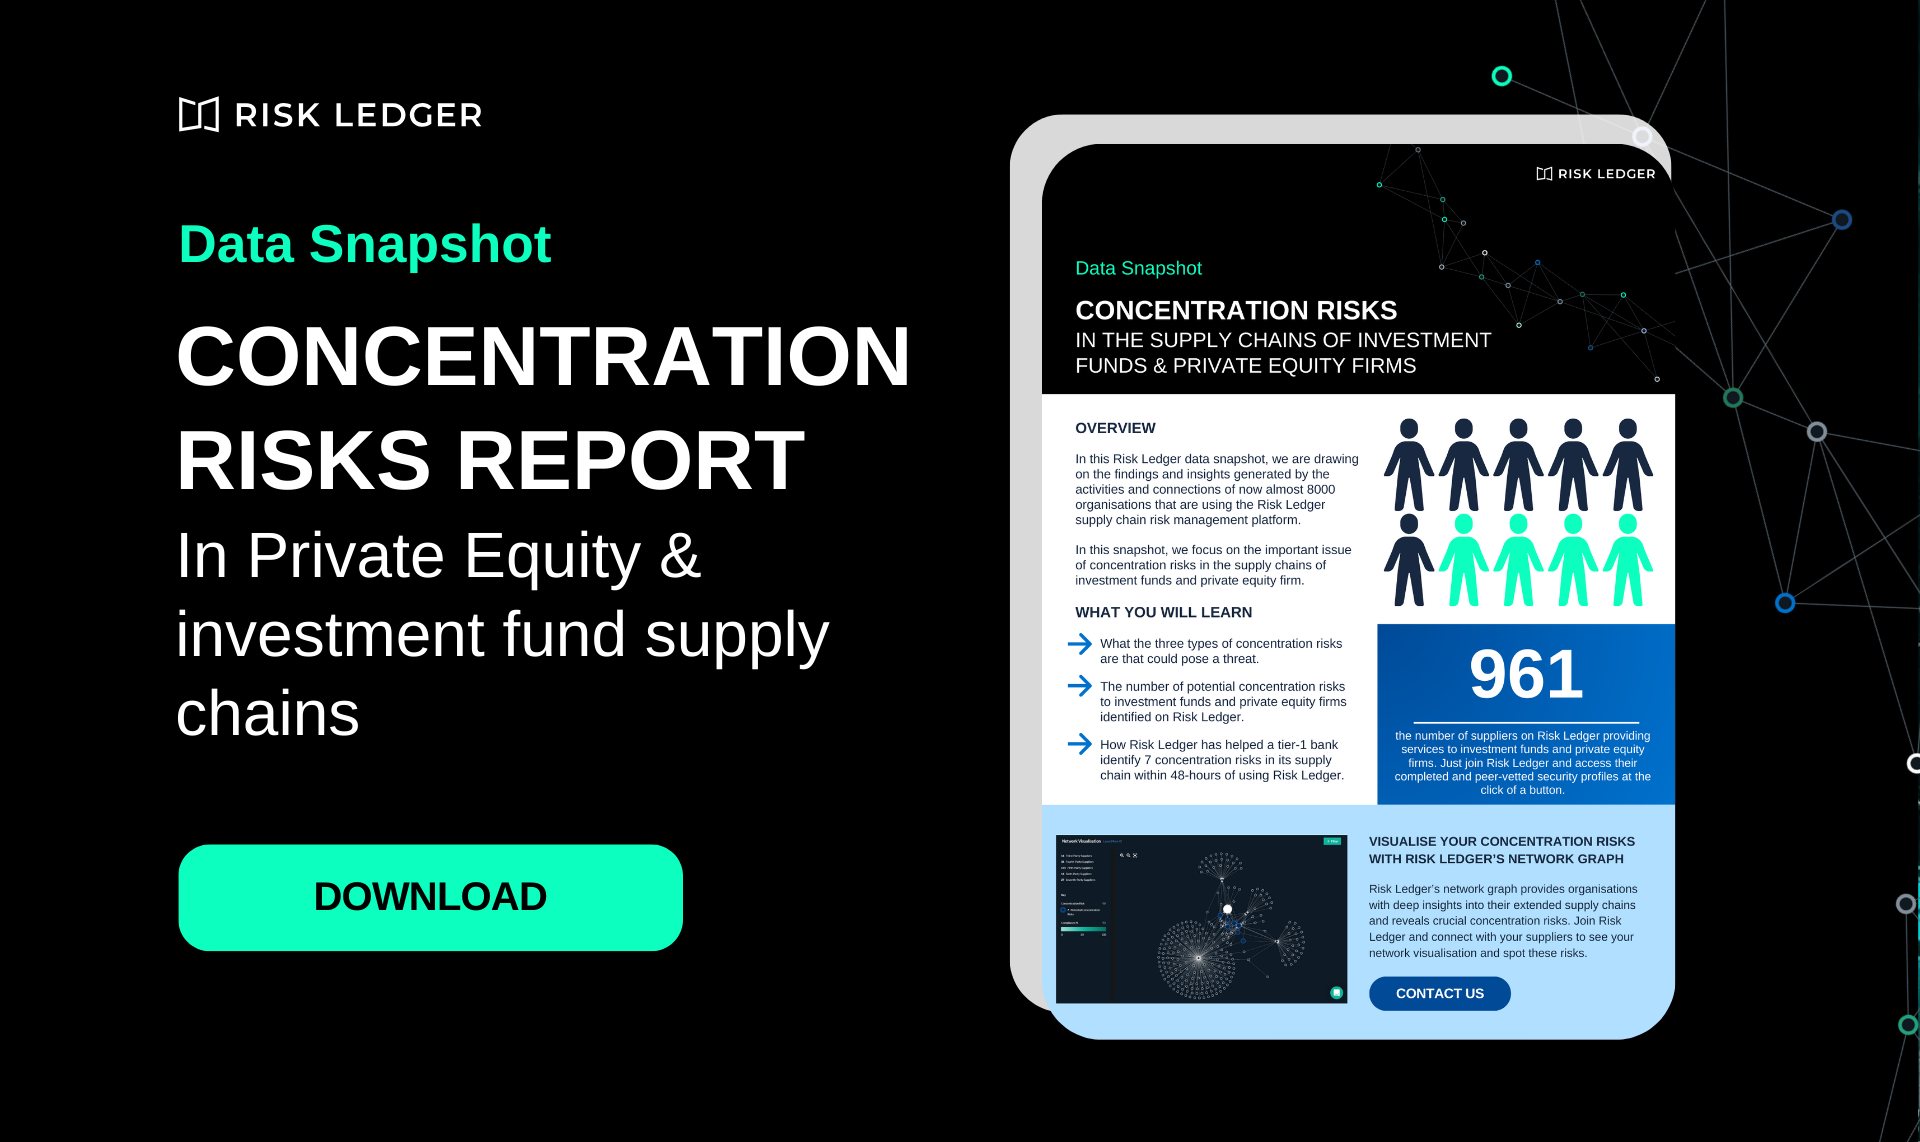
In our recent data snapshot, we identified key concentrations risks for our existing investment fund and private equity clients on our platform.Do you know which concentration risks might be hiding in your extended supply chains?
If you want to learn more about concentration risks, and how Risk Ledger helps organisations uncover and mitigate them, then download our free data snapshot report.
Resources
Data Insights Report
Uncovering Concentration Risks in the Supply Chains of Private Equity Funds: Data Snapshot
In Risk Ledger's latest data snapshot report, we reveal the concentration risks we discovered in the supply chains of our investment fund and private equity clients.

Data Insights Report
More articles

Blog
Cyber Security and Resilience Bill: What It Means for Your Supply Chain
Where the Cyber Security and Resilience Bill stands, a one-table summary, the critical supplier designation test and a 30-day supplier evidence review.
Critical National Infrastructure
Energy
Financial Services
Fintech
Insurance

Blog
Continuous Monitoring of Third-Party Risk in Financial Services
Do financial regulators expect firms to monitor suppliers continuously, or just review them once a year? Learn what DORA, the UK’s Critical Third Parties regime and NYDFS say, what CQUEST does and doesn’t cover, and what recent incidents show about the gap.
Financial Services

Blog
Cyber Security and Resilience Bill: What It Means for Your Supply Chain
Where the Cyber Security and Resilience Bill stands, a one-table summary, the critical supplier designation test and a 30-day supplier evidence review.
Critical National Infrastructure
Energy
Financial Services
Fintech
Insurance

Blog
Continuous Monitoring of Third-Party Risk in Financial Services
Do financial regulators expect firms to monitor suppliers continuously, or just review them once a year? Learn what DORA, the UK’s Critical Third Parties regime and NYDFS say, what CQUEST does and doesn’t cover, and what recent incidents show about the gap.
Financial Services