Supply Chain Visibility: How to See Who Your Suppliers Depend On

How to map the suppliers behind your critical services, find who they depend on, spot what fails together and answer “Are we exposed?” without trying to map everything at once.
Risk Ledger
|
Company
October 15, 2026
|
20
mins read
Supply Chain Visibility: How to See Who Your Suppliers Depend On

Updated 15 October 2026: added tier 2 and tier 3 mapping steps, a dependency mapping template, an “Are we exposed?” checklist and a DORA, FCA, NCSC CAF and NIST frameworks section.

Quick answer

Supply chain visibility is the ability to see which organisations your business services rely on, what those suppliers depend on in turn, and where several of them share the same underlying provider.

  • A supplier list tells you who you buy from. Visibility tells you who those suppliers depend on to deliver the service you receive.

  • Map by business service rather than contract value, starting with one service the business can't afford to lose.

  • A provider that sits behind several of your suppliers is a concentration signal, worth testing for what could fail together.

  • During an incident, a maintained map shows potential exposure quickly. Confirming actual impact still needs current evidence from suppliers.

  • A supplier that hasn't answered is an unknown, not a supplier with no dependencies. Record it as one.

‍

What does supply chain visibility mean for a security team?

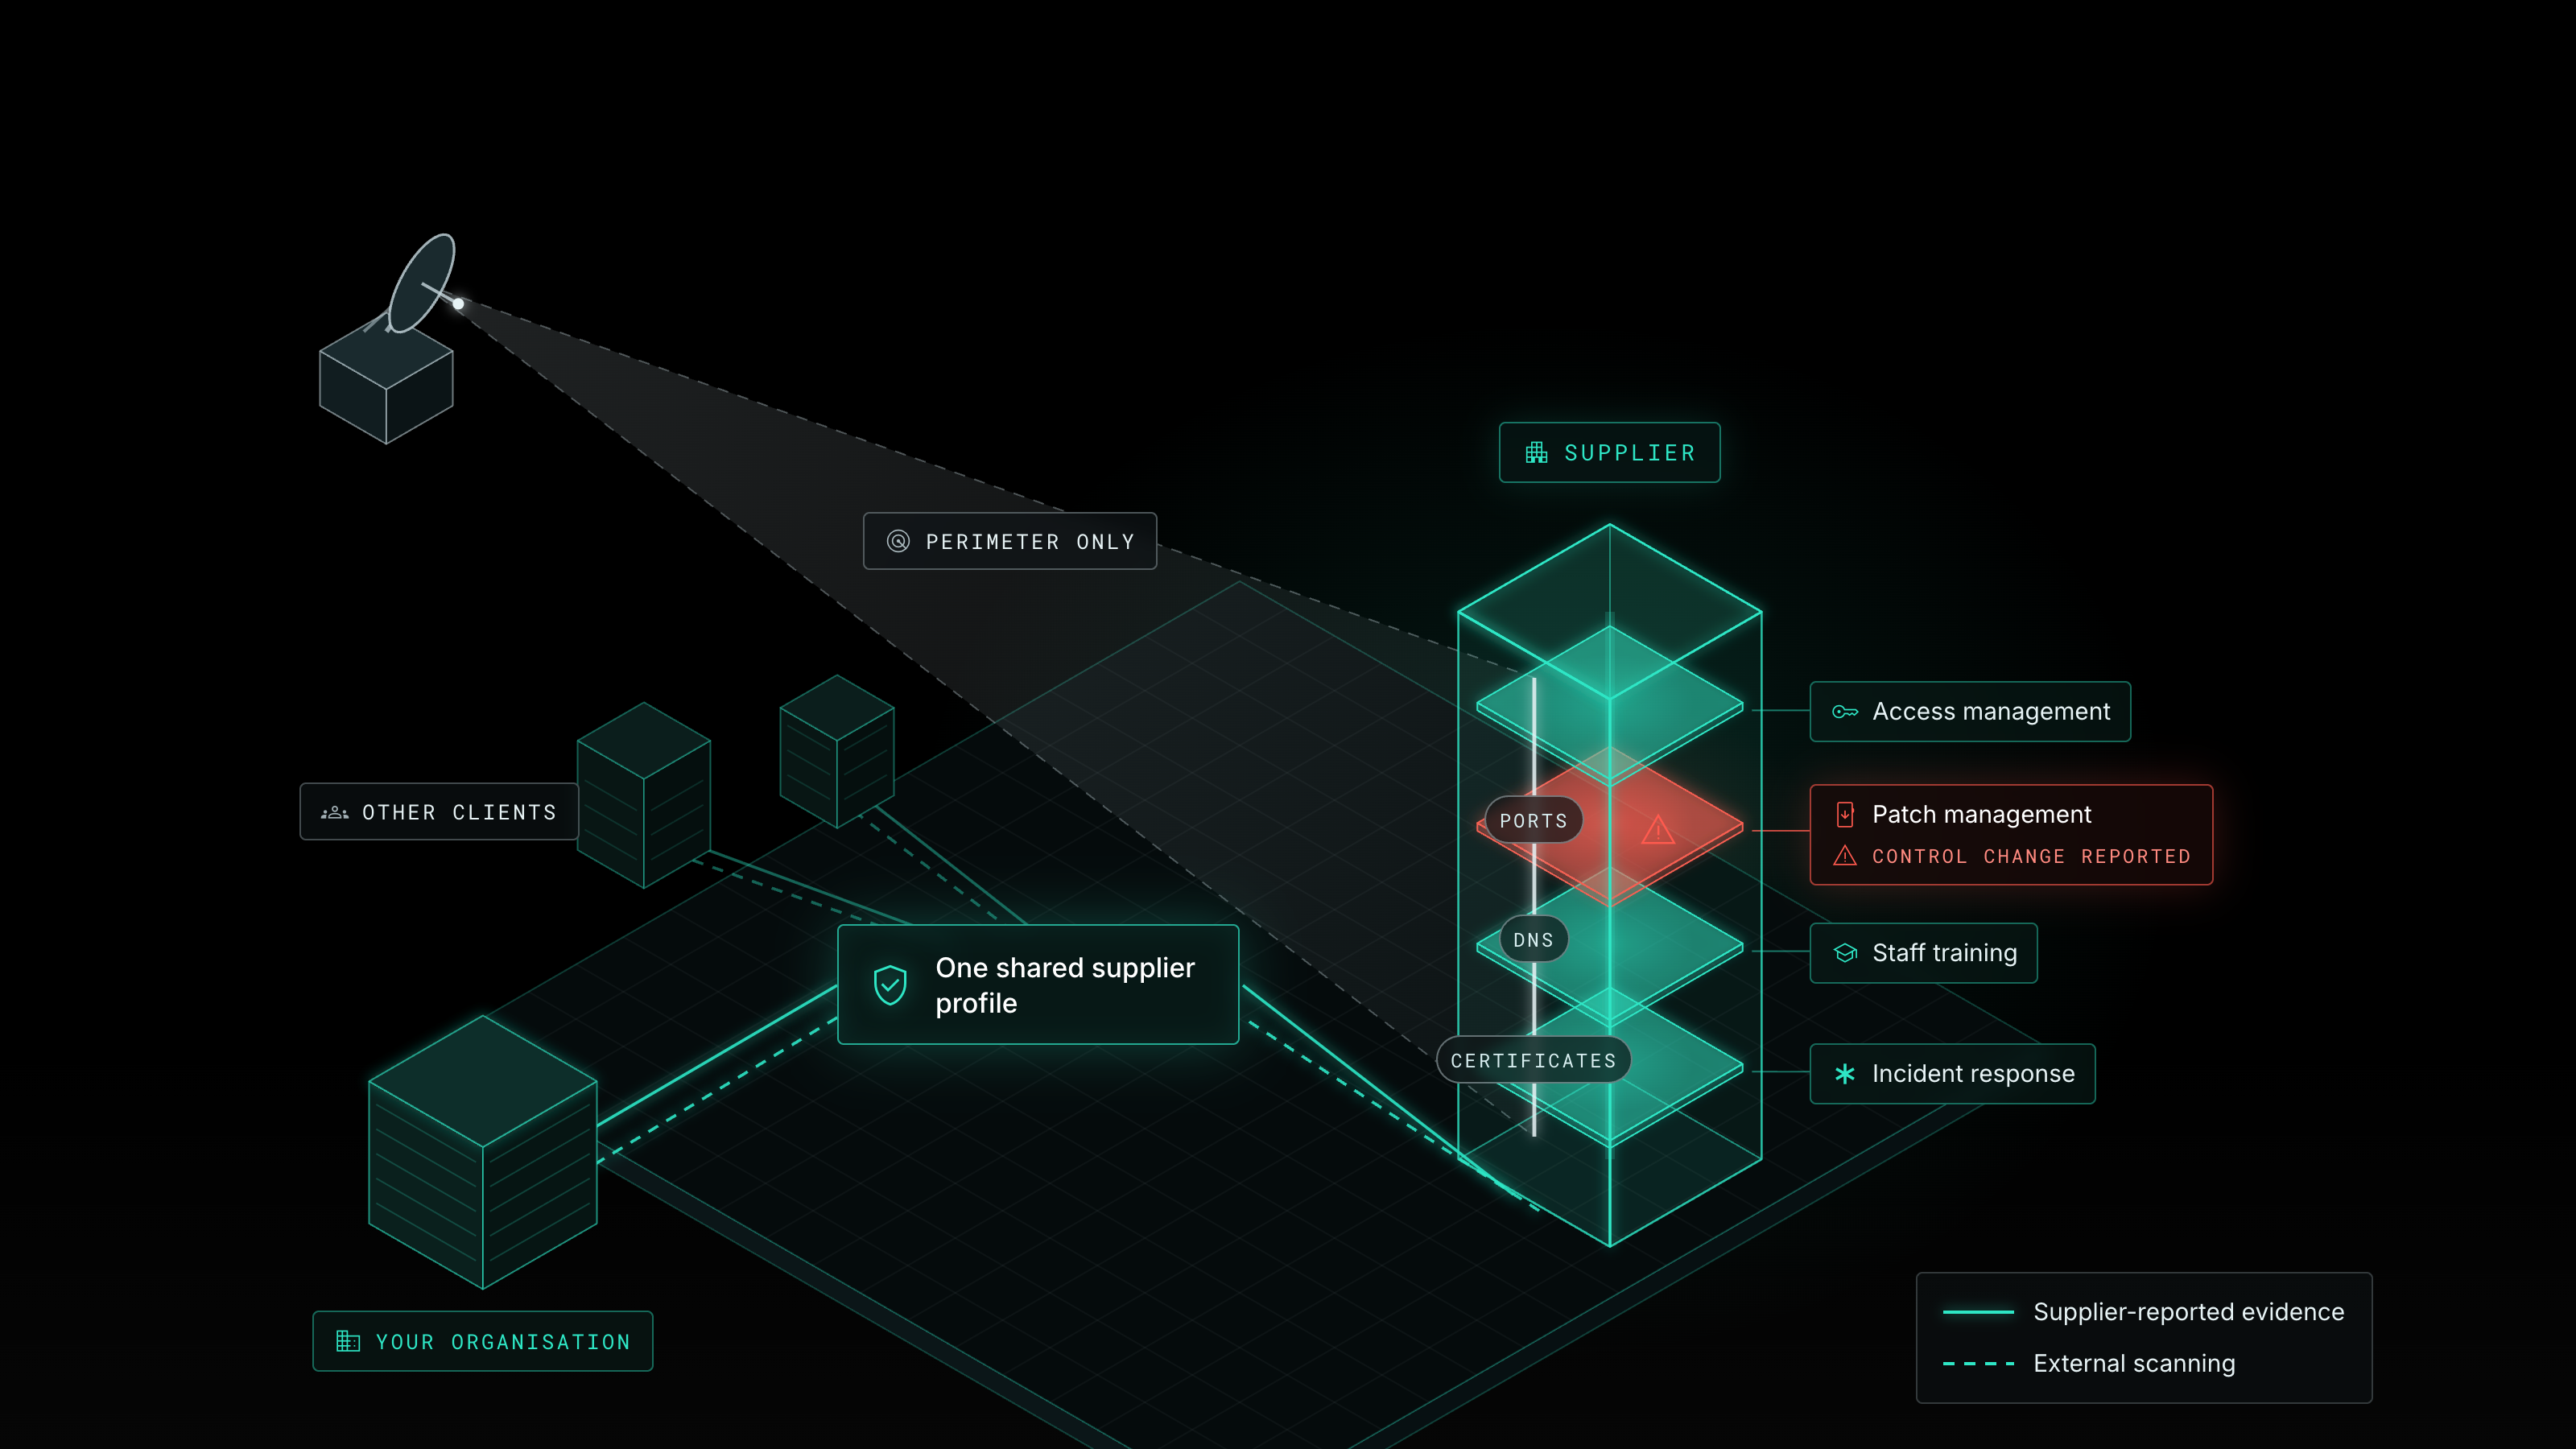
For a security team, supply chain visibility means knowing which suppliers each business service relies on, who those suppliers depend on to deliver it, and where several of them share one provider. Most programmes already cover the first part through their supplier register. The second and third parts sit outside it, and that’s where shared exposure tends to go unnoticed.

NIST describes visibility in two dimensions: how much you can learn about a supplier, product or service, and how far along the supply chain you can learn it. A mature assessment process is usually strong on the first. It can tell you a great deal about each direct supplier, but far less about the providers those suppliers use to deliver your service, because that information sits outside your contracts.

Seeing that second layer changes what a team can answer. With dependencies mapped against business services, you can see where several suppliers rely on the same cloud, software or managed service provider, and test whether those services could fail at the same time. You can check whether a backup supplier is really independent of the primary, or whether both run on the same platform. When a provider announces an incident, you can narrow the first round of outreach to the suppliers actually connected to it, rather than emailing everyone on the register. And when leadership or a regulator asks which suppliers matter and why, the answer rests on the services they support, not on contract value.

The limits are just as practical. Anything beyond your direct suppliers depends on what they know and are willing to share, so it arrives incomplete and needs a source and a date recorded against it. Relationships also change between reviews. Mapping every supplier to the same depth takes more effort than most teams have, which is why the workable version starts from the services the business can’t afford to lose.

‍

Do you know who your suppliers depend on? How to find nth-party suppliers

Find nth-party suppliers by asking each direct supplier which providers it relies on to deliver the specific service you receive, then repeating the question for the providers that matter most. Record each relationship with its source and the date it was confirmed. Tier 1 is your direct supplier, tier 2 is their provider, and tier 3 is the provider behind that.

A fourth party is a provider your direct supplier relies on to deliver the service you receive. You hold no contract with it, so it rarely appears on your register.

That’s how an organisation ends up breached by a company it never signed a contract with. In June 2023, British Airways, the BBC and Boots each reported that staff personal data had been exposed through their payroll provider, Zellis. Zellis had been compromised through a vulnerability in MOVEit Transfer, the file-transfer software it used, and later confirmed that eight UK organisations had data stolen. British Airways described the incident as occurring via one of Zellis’s own third-party suppliers. The software sat one step beyond the contract each employer held.

Supply chain visibility

The tiers, and what most programmes see by default

Tiers describe distance from your organisation. Most programmes have built tier 1 properly. Visibility usually thins out from tier 2 onwards.

The tiers of supply chain visibility, what each shows by default and what typically goes unseen.
TierWhat you can usually seeWhat's typically missingWhy it matters
Tier 1: direct suppliers (third parties) Suppliers you hold a contract with, on your register and assessed through your process. Little, although suppliers onboarded without security's involvement can still be absent. Tells you who you buy from, not what they depend on.
Tier 2: fourth parties Little by default, unless a supplier has told you or a contract lists subprocessors. The hosting, software, managed service and subcontracting providers your direct suppliers use to deliver your service. An incident here can reach you without touching any supplier you assess directly.
Tier 3: fifth parties Almost nothing by default. The providers behind your fourth parties. Worth mapping where a critical service depends on that path.
Nth parties Nothing by default. Dependencies further along the chain. Investigate case by case, when impact or uncertainty justifies the effort.

Concentration risk isn't a tier. It's what appears when the same provider sits on several of these paths at once. See what fails together.

Practical decision rule

If you can answer tier 1 questions confidently today, that's normal. Map tier 2 for the services you can't afford to lose before going deeper, and record the path as well as the provider, because the same company can sit at tier 1 for one service and tier 2 for another.

Tier describes a relationship, not a type of company. A large cloud provider can be your tier 1 supplier for one service and tier 2 for another, sitting behind a SaaS supplier you contract with separately. That’s why a useful record names the path (“Supplier A uses Provider B to host Service C”) rather than the provider alone.

Discovery works one service at a time. Start with the suppliers behind a service the business can’t afford to lose, and ask each one which providers are needed to deliver that service to you, rather than for a list of every organisation it buys from. Hosting, managed service providers, critical software, identity and data-processing subcontractors cover most of what matters. Record each answer against the supplier, the service and the date. Then take the providers whose failure would hurt a critical service and repeat the question for them. Tier 3 is worth reaching only on those critical paths. Expect gaps along the way. A supplier may not know its own providers’ providers, or may not be able to share them, and that unknown is worth recording rather than leaving blank. The full question set, including what to do when a supplier won’t disclose, is in our guide to fourth-party vendor risk management.

Declared dependencies have a clear job and a clear limit. They’re good evidence for resilience and concentration work, because suppliers know which platforms they run on. They won’t expose an organisation that is determined to hide a relationship. For critical suppliers, check declared links against contracts, published subprocessor lists and direct questions.

In our Every Link Matters 2026 survey of 500 UK security and third-party risk professionals, lack of visibility beyond direct third parties was the most common answer when respondents named the biggest shortcoming in their current approach.
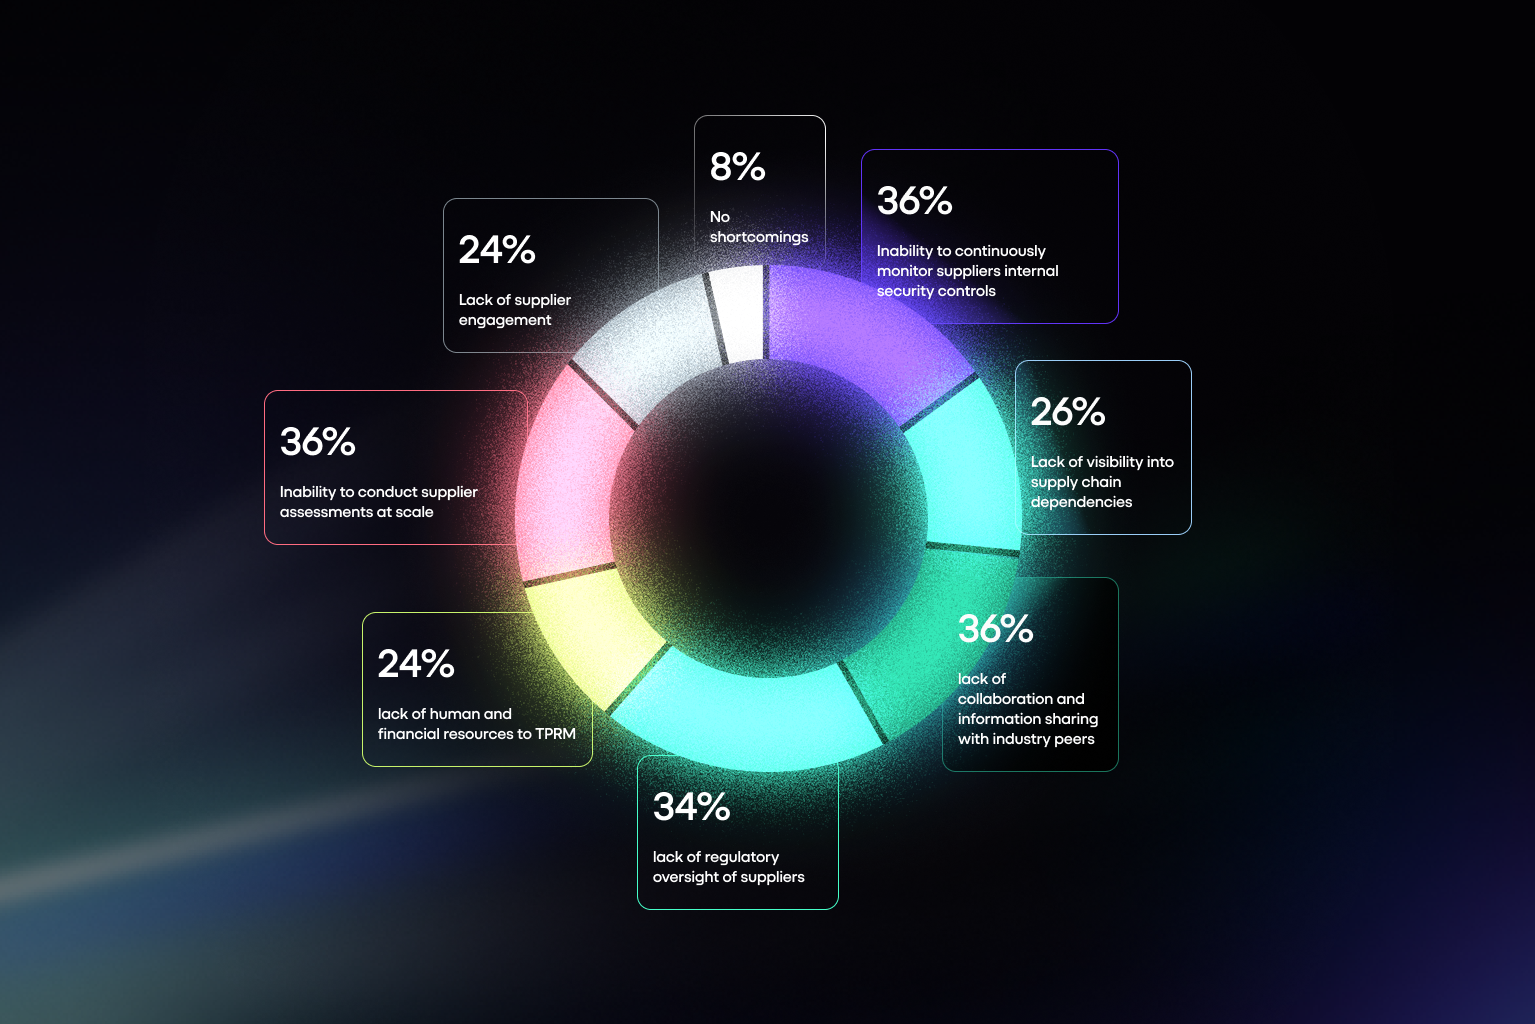
Supply chain visibility survey results

Why do tier 2 suppliers create compliance risk?

Tier 2 suppliers create compliance risk because obligations you hold often extend to providers you never contracted with. If a supplier processes personal data on your behalf, UK GDPR requires it to get your prior written authorisation before engaging a sub-processor, so you need to know who those sub-processors are.

For financial entities in scope of DORA, Article 29(2) requires an assessment of whether long or complex subcontracting chains could affect their ability to monitor the functions they’ve contracted out, and their regulator’s ability to supervise them. That applies to ICT services supporting critical or important functions.

Both obligations are scoped. UK GDPR covers personal data processed on your behalf, and DORA covers in-scope financial entities and the ICT services behind their critical or important functions. Within those limits, an unmapped tier 2 provider is a gap a regulator or auditor can reasonably ask about.

‍

What is concentration risk? How to see what fails together

Concentration risk is exposure that builds up when several of your suppliers rely on the same provider, or on closely connected providers, so one failure can disrupt them together. To detect it, map each critical supplier’s dependencies in one place and look for providers that repeat. Spreadsheets can show this supplier by supplier, but a network map makes what fails together much easier to see.

Two things are easy to blur here. A shared provider is a signal: the same name sits behind more than one of your suppliers. A shared failure scenario is the risk: one plausible event at that provider would affect several of your services at the same time. Most of the work is getting from the first to the second.

Detection starts with the map from the previous step. For each critical business service, list the providers behind its suppliers. Put them in one view, normalise the names so a trading name, a product and a parent company don’t appear as three different entries, and flag any provider that appears under two or more suppliers.

Then take each flag and test it:

  • Which services depend on that provider?
  • Would a realistic outage or compromise hit them all at once, or do they use different regions, environments or products?
  • How long could each service tolerate the disruption, and does a usable alternative exist?

A repeated name that fails this test is a dependency you’ve documented. One that passes it is a concentration you need to act on.

Worked example (fictional)

One service, four suppliers, one shared provider

A firm maps the suppliers behind its customer onboarding service, then adds who each of them depends on. Switch on the outage to see what fails together.

  1. 1List the suppliers behind each critical service.
  2. 2Add the providers each supplier depends on.
  3. 3Flag any provider that appears more than once.
  4. 4Test a realistic failure at that provider.
Dependency map for a fictional customer onboarding service Customer onboarding uses suppliers A, B and C. Its fallback uses supplier D. Suppliers A, B and D are all hosted on provider X. Supplier C uses identity provider Y for staff access. BUSINESS SERVICE DIRECT SUPPLIER THEIR PROVIDER Customer onboarding ● Running ● Down Onboarding fallback ● Ready ● Down Supplier A Verification Supplier B Workflow Supplier C Support Supplier D Backup verifier Provider X Cloud hosting Behind 3 suppliers Provider Y Identity / access

Provider X appears under three suppliers, including the backup. On a supplier-by-supplier list, that repeat is easy to miss.

Provider X goes down. Suppliers A and B lose hosting at the same time, so customer onboarding stops, and the fallback can't take over because supplier D runs on provider X too. Supplier C keeps running on provider Y, but onboarding can't complete without A and B.

In this example, verification supplier A, workflow supplier B and backup verification supplier D are all hosted on cloud provider X. Support supplier C relies on identity provider Y for staff access.

What the map tells you
  • There's a potential shared hosting exposure across three suppliers.
  • The fallback may not be independent of the primary.
  • There's a separate access dependency on provider Y to look at.
What it doesn't tell you yet
  • Whether all three use the same region or environment at provider X.
  • Whether a realistic outage would affect each one in the same way.
  • Whether failover to supplier D has ever been tested.
Practical decision rule

Treat a repeated provider as a question to answer, not a finding to report. Confirm each relationship for your service, test the failure scenario against each one, then decide whether to accept, mitigate or reduce the dependency.

Acting on it doesn’t automatically mean switching providers. Moving away from a shared platform brings migration risk, new suppliers to assure and, sometimes, a different concentration you hadn’t mapped. Depending on the scenario, the better answer may be tested recovery, tighter notification terms, stronger assurance on the provider, or a documented decision to accept the exposure.

Our guide to concentration risk covers the options in more depth.

Free assessment

Where does your supply chain stand?

Answer a short set of questions about how you manage suppliers today and get a directional view of where your approach could leave you exposed.

It works from your answers, so it won't map your actual suppliers.

When your backup supplier shares the same dependency

A failover plan usually assumes the primary and backup suppliers are separate risks. If both run on the same underlying platform or software, an incident that takes down the primary can take down the backup at the same time, for the same reason, which defeats the point of having one.

The check is specific. Ask where the backup is hosted, whether its recovery environment, credentials or management tooling depend on the same provider as the primary, and whether the switch has ever been tested. Two contracts with two suppliers only give you independent resilience if the scenario that disables one leaves the other running.

Full guide here: Are Our Backup Suppliers Actually Independent?

‍

Which suppliers can take you down? Deciding criticality by business service

Decide supplier criticality by starting from your business services, not your supplier list. For each service, identify the suppliers it depends on, then judge what happens if each one becomes unavailable, compromised or unreliable. Weigh the data and access it holds and whether a workable alternative exists. Contract value alone doesn’t tell you how much harm a supplier incident could cause.

A critical supplier is one whose failure or compromise would stop, or seriously damage, a service the business can’t afford to lose.

Synnovis shows the shape of it. The company provides pathology services to NHS trusts in south east London. After a ransomware attack on 3 June 2024, King’s College Hospital and Guy’s and St Thomas’ rearranged more than 800 planned operations and 700 outpatient appointments in the first week, and pathology services in the area ran at around 10% of normal capacity. The incident sat with a supplier, but the consequences landed on the clinical services that depended on its tests.

Criticality also depends on knowing the supplier exists. In many organisations, a large share of digital buying happens outside security’s view. A team signs up to a tool, procurement onboards it on commercial terms, and security finds out later, if at all.

Tiers set by procurement tend to reflect contract value and commercial importance, which is a reasonable lens for procurement and a poor one for security. A low-cost identity service can lock staff out of several systems at once. A small provider holding sensitive personal data can be critical for confidentiality even if its outage wouldn’t stop anything. The fix is mostly about timing, rather than tooling. An early relationship with procurement means security hears about a new supplier before the contract is signed, and service owners can say what would actually break. Security shouldn’t be expected to infer every operational consequence on its own.

Assess the engagement, not just the company. The same supplier can provide a minor administrative tool and a system the business depends on, and a single company-level rating blurs the two. Public sector security teams we speak to describe it this way, assuring the engagement rather than the supplier. Record criticality against each service a supplier delivers.

Supplier criticality

Contract value vs service impact

Both are legitimate ways to rank suppliers. They answer different questions, and only one tells you which suppliers could take a service down.

How tiering by contract value differs from tiering by impact on a business service.
Tiering by contract valueTiering by service impactWhat changes
Prioritises the suppliers you spend most with. Prioritises the suppliers whose failure would cause most harm. Low-cost but indispensable suppliers stop slipping through.
Treats a supplier as one commercial relationship. Looks at each product or engagement the supplier delivers. Different services from the same supplier get different scrutiny.
Reflects importance to procurement. Considers availability, confidentiality and integrity. Security and operational exposure become visible.
Often assumes a replacement could be found. Tests how long a replacement or workaround would take. Exit plans and workarounds become practical questions.
Practical decision rule

If losing a supplier would stop a critical service, make it untrustworthy or expose sensitive data, treat that supplier as critical whatever it costs. If a large contract supports something the business could pause for a week without real harm, it isn't critical for security purposes.

Keep criticality separate from control strength. A critical supplier can have excellent controls, and a supplier with weak controls can support something you could do without for a week. Criticality decides how much assurance and mapping effort a supplier gets. The assessment decides what that assurance finds. Ratings are judgements and will be wrong at the edges, so revisit them when a service changes rather than treating the score as the deliverable.

NIST IR 8276 lists knowing and managing critical suppliers among its key supply chain practices.

For a structured way to score this, use our supplier criticality matrix, or read how to identify critical suppliers in your supply chain.

‍

How do you map tier 2 and tier 3 suppliers in practice?

To map tier 2 and tier 3 suppliers, start with one critical business service, list its direct suppliers and rank them by criticality. Then ask the critical ones which providers they need to deliver that service to you, and repeat the question only where a tier 2 provider supports a critical path. Record each relationship with its source and date in one shared map, so repeated providers become visible.

The method below is service-led. It maps what one service depends on, rather than everything every supplier uses. That keeps the effort proportionate and gives each finding a business consequence attached.

  1. Pick the service and the question. Choose one service the business can’t afford to lose, and frame the decision: if the suppliers behind it were disrupted, could we keep delivering it within tolerable limits?
  2. Reconcile the direct suppliers. Combine the procurement register with accounts payable, SaaS and IT inventories, data processing agreements and what service owners know. No single source will be complete. Suppliers onboarded without security are the ones most often missing.
  3. Record the engagement. For each supplier, note the product or service bought, the data it handles, the access it holds and who owns the relationship.
  4. Rate criticality with the service owner. Judge availability, confidentiality and integrity impact, how long the service could tolerate disruption, and whether a workaround exists.
  5. Ask critical suppliers for service-specific dependencies. Ask for the providers needed to deliver your service, not every organisation they buy from.
  6. Record relationships, not names. “Supplier A uses Provider B to host Service C” is useful. “Supplier A uses Provider B” isn’t. Attach the source and the date confirmed.
  7. Normalise names and flag repeats. Merge trading names, product names and parent groups, then flag any provider that appears under more than one supplier. A repeat is a concentration signal to test.
  8. Go to tier 3 only on critical paths. Repeat the question for tier 2 providers whose failure would hurt a critical service. Then test the realistic failure scenario for each flagged overlap.
  9. Decide, assign and maintain. Every flag ends in an owner and a decision: improve assurance, test a fallback, tighten notification terms, reduce the dependency or accept it on record. Update the map when something material changes, and keep a proportionate scheduled check as well.

Expect the map to be incomplete, and design for that. Suppliers won’t always know their own providers’ providers. Some will decline to share names for commercial or security reasons. Others won’t answer at all. A blank cell hides all three situations. A recorded status (“unknown”, “declined”, “awaiting reply”) keeps them visible and lets you escalate by criticality. Non-response tells you only that you don’t know. It doesn’t mean the supplier has no dependencies, and it doesn’t prove poor security.

For a critical supplier, try a confidential sharing route or a service-level summary, check contractual and published subprocessor information, and ask about resilience characteristics even when names are restricted. If the gap still stands, it becomes a finding with an owner, which is a more defensible position than a map that silently assumes the gap away.

Not sure where your gaps are? Run the Supply Chain Risk Exposure Assessment for a directional view of where your current approach leaves you exposed. It works from your answers about how you manage suppliers today, so it won’t discover your actual suppliers or confirm your map.

What supplier data do you need at each tier?

Collect less at each tier as you go further out, and only for the paths that matter.

  • Direct suppliers: the service delivered, the business service it supports, data handled, where it’s hosted, key software (including any AI model provider), and material subcontractors.
  • Tier 2: the provider’s name, its role (hosting, software, managed service, identity, AI model), which of your services it touches, and whether a fallback shares it.
  • Tier 3: collect only for critical paths. Record the provider, its role and the path it sits on.

Send this as a targeted dependency request rather than another full security questionnaire. Four questions cover most of it:

  • Which external providers are necessary to deliver this service to us?
  • What does each one do?
  • What would happen to our service if that provider were unavailable?
  • How would you tell us about a material change or incident at one of them?

Reuse the assurance evidence you already hold from your supplier risk assessment rather than asking for it again.

The full question set, with follow-ups for critical paths, is in our guide to fourth-party vendor risk management.

A mapping template you can start with

Use one row per dependency relationship, not one row per supplier. A supplier with three relevant providers gets three rows, and that’s what makes repeats easy to find. The template records the relationship, its impact, the evidence behind it and the action it needs. NIST SP 800-161 Rev. 1 treats a supplier inventory as its own control (SR-13). This template extends that inventory to the providers behind your suppliers.

Template

Dependency map: one row per relationship

Set these columns up in a spreadsheet or your TPRM platform, and add one row for every supplier-to-provider relationship behind a service.

  • 16 columns
  • 4 groups
  • 1 row per relationship

1The relationship

  • ABusiness serviceConnects the row to something the business can't afford to lose.
  • BDirect supplierThe relationship you manage and contract with.
  • CProduct or engagementSeparates a minor tool from a critical system at the same supplier.
  • DProvider nameThe upstream organisation, normalised to one name.
  • EProvider roleHosting, software, managed service, identity, AI model or subcontractor.
  • FTier and pathTier 2 or 3, and which supplier it sits behind.

2The impact

  • GCriticalityWhat happens to the service if this relationship fails.
  • HData or access involvedSupports the confidentiality and integrity judgement.
  • IEnvironment or locationRegion or deployment, which decides whether failures overlap.
  • JFallback or workaroundWhat takes over, and whether it shares this provider.

3The evidence

  • KSourceSupplier declaration, contract, subprocessor list or technical evidence.
  • LEvidence statusHow far you can rely on the row (see below).
  • MDate confirmedMakes freshness visible at a glance.

4The action

  • NRelationship ownerThe person who keeps this row current.
  • OAlso used byOther suppliers behind which the same provider appears.
  • POpen question or actionWhat has to happen next, so the map drives decisions.

Evidence status values (column L)

  • DeclaredThe supplier says the relationship exists.
  • CorroboratedA contract or subprocessor list supports it.
  • InferredAn indication, not yet confirmed for your service.
  • UnknownNot obtained, declined or awaiting a reply.
  • DisputedSources conflict and need resolving.

Example row (fictional)

ABusiness service
Customer onboarding
BDirect supplier
Verification supplier A
CEngagement
Identity checks API
D·EProvider
Provider X, hosting
FTier and path
Tier 2, behind supplier A
GCriticality
Critical: onboarding stops without it
HData or access
Customer identity documents
JFallback
Supplier D, which also uses provider X
K·LSource and status
Supplier declaration, declared
MDate confirmed
The date you received it
OAlso used by
Suppliers B and D
PNext action
Confirm region, test failover to D
Practical decision rule

If a row has no source, no date or no owner, treat it as unknown. A map you can't trace back to evidence won't hold up when leadership, an auditor or an incident tests it.

If you have a small team

Start with one critical service and work through steps 1 to 6 for its direct suppliers, stopping at tier 2. Go deeper only where impact, uncertainty or a repeated provider justifies it. A partial map built around the services that matter answers more useful questions than a complete register that can’t say what depends on what.

‍

Are we exposed? Using supply chain visibility when a supplier is breached

A maintained dependency map, whether it lives in a spreadsheet, a resilience mapping exercise or a TPRM platform, helps answer “Are we exposed?” by narrowing the first round of investigation. When a provider announces an incident, it shows which of your suppliers are linked to it and which business services they support. The map shows potential exposure. Current evidence from suppliers confirms actual impact.

Without that record, the first hours of an incident tend to go the same way. The security team emails every supplier that might be relevant, asking whether they use the affected product. Each supplier is fielding the same question from many of its own customers at once, so replies are slow and uneven. Answers arrive in different formats, some simply say “we’re investigating”, and the team pieces the picture together by hand while leadership waits.

Nothing in that process is careless. It’s what one-to-one outreach looks like under pressure. Knowing your dependencies in advance changes the starting point rather than the effort involved. You already know which suppliers sit near the affected provider, which services they support and who to contact, so the first messages go to the critical few rather than the whole register.

The response gap

Where the first moves go when a provider is breached

Same incident, same team. The difference is what you already know when the news breaks, whether it's held in a spreadsheet, a resilience mapping exercise or a platform.

Incident response starting from a supplier register compared with starting from a maintained dependency map.
StepStarting from the supplier registerStarting from a dependency map
First question Which of our suppliers might use this? Which suppliers are linked to this provider, and for which services?
Who you contact Everyone on the register who might be relevant. The suppliers behind critical services, first.
What you ask A general "are you affected?" Specific questions about the product, version and your environment.
What comes back Answers in different formats, at different speeds. Answers recorded against relationships you already know.
What you can tell leadership "We're still finding out who's involved." Which services are potentially exposed, what's confirmed and what's still unknown.
Practical decision rule

The map shortens the search, not the verification. Use it to decide who to ask first, then rely on current evidence from those suppliers to decide what you report.

The FCA’s review of the July 2024 CrowdStrike outage supports this. The outage was caused by a defective Falcon content update for Windows hosts, not a cyber attack. The FCA found that firms with detailed mapping of their third and nth party relationships could understand their exposure quickly and take mitigating action. Firms with existing routes for sharing information with third parties responded faster. Firms whose contracts set out clear responsibilities received information from affected third parties more effectively.

Supplier-level mapping has a limit, and Log4j shows where it sits. Log4j is an open-source logging library built into applications and services. NCSC’s advice to organisations unsure whether they used it was to ask their developers and third-party suppliers. A record of supplier relationships tells you which suppliers to ask. It can’t tell you whether a vulnerable component, version or configuration is present in the product you use. For that you need component-level evidence, such as version information, a software bill of materials where one exists, and the supplier’s confirmation that it has remediated.

The “Are we exposed?” checklist

  1. Establish what happened. Record the affected provider or product, the type of incident, any versions or services named, the authoritative source and when it was last updated.
  2. Find the potentially relevant paths. Use your dependency map to list direct suppliers linked to the provider, any deeper relationships, the business services they support and the data or access involved.
  3. Verify relevance and impact. Ask each linked supplier:
    • whether it uses the affected product for your service
    • whether your environment is in scope
    • whether disruption or data exposure has been confirmed
    • when its next update is due
  4. Prioritise action. Contact the suppliers behind critical services first. Check workarounds, whether backups are independent of the affected provider, recovery status, and any contractual or regulatory notification duties.
  5. Report honestly. Give every linked supplier a status, and record its answers in the same place as your dependency map so the next incident starts from a better position.

Use a small, fixed set of statuses: potentially relevant, exposure confirmed, impact confirmed, not affected (with evidence), still unknown, and mitigated. Never record “no reply” as “not affected”.

A quick leadership update template:

“We have identified [number] supplier relationships supporting [services] that are potentially linked to [provider]. [Status] is confirmed for [suppliers]. [Gaps] remain under investigation. We have prioritised [actions] and will give the next update at [time].”

For the full response process, including containment and notification, see our third-party incident response playbook.

‍

Supply chain visibility vs transparency, traceability and assurance

Supply chain visibility is what you can see about the organisations and dependencies behind your services. Transparency is what an organisation discloses to others. Traceability follows the origin and path of a specific product or component. Assurance is evidence-based confidence that suppliers meet the requirements that matter. In everyday use the terms overlap, but each one answers a different question.

They’re used interchangeably often enough that NIST’s glossary lists transparency as a synonym for visibility. For security teams, though, the distinction is worth keeping, because each term points to a different kind of evidence and a different gap.

Four different questions

Visibility, transparency, traceability and assurance

The terms overlap in everyday use. For a security team, each points to a different kind of evidence.

  • Visibility

    What you can see

    Who do our services depend on, and where do those dependencies overlap?

    Typical evidence

    A dependency map linking suppliers, their providers and the services they support.

    Gap it exposes

    Shared providers and fallbacks that aren't independent.

  • Assurance

    What you can rely on

    Is this supplier meeting the security requirements that matter for our service?

    Typical evidence

    Assessment answers, certifications, policies and verified supporting evidence.

    Gap it exposes

    Weak or unverified controls at a supplier you depend on.

  • Transparency

    What they disclose

    What has this supplier chosen to share about how it operates?

    Typical evidence

    Trust centres, published subprocessor lists, shared reports and certificates.

    Gap it exposes

    Usually general rather than specific to the service you receive.

  • Traceability

    Where it came from

    What is the origin and path of this specific product or component?

    Typical evidence

    In security, component-level records such as a software bill of materials.

    Gap it exposes

    Whether a vulnerable library or version sits inside a product you use.

Practical decision rule

Most programmes are strongest on assurance for direct suppliers. If you can say how secure a supplier is but not what it depends on, the gap is visibility, and another assessment won't close it.

Transparency is the supplier’s side of the exchange. A trust centre, a published subprocessor list or a shared certification is the supplier choosing what to disclose. That’s useful, and it’s often where visibility starts. But what a supplier discloses to everyone is rarely specific to the service it delivers to you. Traceability belongs mostly to logistics and compliance, where it means following a product or material back to its source. The nearest security equivalent is component-level evidence, such as a software bill of materials, which matters when the question is whether a particular library or version sits inside a product you use.

Visibility and assurance are the two that get confused most often. Assurance tells you how well a supplier is managing its own security. Visibility tells you what that supplier depends on and how it connects to the services you can’t afford to lose.

A supplier can pass every control in your assessment and still run your service on the same hosting provider as three of your other suppliers. Even strong assessment wouldn't show that, because the assessment wasn’t asking. A completed questionnaire records a supplier’s answers about its own controls, and whether those answers amount to compliance or meaningful assurance depends on the requirements, the supporting evidence, the scope and whether anyone has verified them. The point is that assurance and visibility do different jobs, so a programme strong in one can still be blind in the other.

‍

How do you keep supply chain visibility current?

Keep supply chain visibility current by giving every critical relationship an owner, a confirmation date and a set of triggers that prompt a review, alongside a proportionate scheduled check. An assessment or dependency map is a snapshot. What matters is how you’ll find out when the picture behind it changes.

An assessment is a snapshot, not a countdown. A record can stay accurate for months, and many do. The risk lies elsewhere. Suppliers change hosting, add subcontractors, release features and get acquired between reviews, and nothing in an annual cycle is designed to notice. In our conversations with financial services teams, a recurring pattern is a supplier spreadsheet rebuilt for each review cycle, which is accurate on the day and then left to age. Public sector teams describe a similar shape: assurance that’s thorough up to contract signature, then largely stops. Neither is a failure of effort. Both are programmes built around scheduled collection rather than change detection, and the fix is to add the second without abandoning the first.

Common mistakes

Two things that feel like currency

Both are sound practices. Neither, on its own, tells you when the picture has changed.

  • 1Feels current

    "We reassessed every critical supplier this year."

    What it can miss

    Changes between reviews: a new subcontractor, a hosting move, an acquisition or a new feature. The assessment was accurate on the day it was completed.

  • 2Feels current

    "The supplier told us who its providers are."

    What it can miss

    Whether that answer is still true, and who will tell you when it isn't. A declared dependency needs an owner, a date and a route for updates.

Practical decision rule

If a critical relationship has no owner and no review trigger, its last confirmed date is the only thing telling you it's still true. Fix that before adding more suppliers to the map.

Three things keep a relationship current.

An owner: Name the person who will notice when it changes, usually whoever manages the supplier relationship, with the service owner confirming impact.

Triggers: Define the events that prompt a review before the scheduled date:

  • a material change to the service
  • a new subcontractor or hosting arrangement
  • an acquisition or change of ownership
  • a new AI feature
  • an incident
  • changed recovery arrangements
  • expired assurance evidence

A route for the supplier to tell you: Agree notification terms for material changes in the contract, so updates don’t depend on you asking at the right moment.

Ownership changes deserve a specific mention. An acquisition can move hosting, change subcontractors or shift where data is processed, without anything changing in the service you see.

This doesn't replace a scheduled check. Change-driven updates rely on someone noticing or telling you, and both can fail. A proportionate periodic review, more frequent for critical suppliers, catches what the triggers miss. Supplier-maintained information and automated signals have coverage limits too. Continuous monitoring is valuable, but it can’t show you a change nobody recorded.

When an existing supplier adds AI

An existing supplier can introduce a new dependency simply by adding an AI feature. Your original assessment may not have covered that feature’s model provider, its data flows or how it behaves when that provider is unavailable.

Treat it like any other material change and ask:

  • Is the feature used in the service you receive?
  • Who provides the model or hosts it?
  • What data is sent to it, and where is it processed?
  • What retention and training terms apply?
  • What happens to your service if the model provider is unavailable?
  • Can the feature be switched off for your organisation?

Don’t assume the answers. Not every AI feature sends data to an outside provider, and terms differ between providers and contracts. The aim is to bring the feature into your dependency map like any other provider, not to treat AI as a separate category of alarm.

‍

Which frameworks expect you to map supplier dependencies?

Several frameworks expect you to understand the suppliers behind your critical services, and some reach into subcontractors:

  • DORA requires in-scope financial entities to record the subcontractors that underpin ICT services supporting critical or important functions.
  • FCA and PRA rules require firms to map the resources behind each important business service, including those provided by third parties.
  • NCSC’s Cyber Assessment Framework and NIST guidance set similar expectations as assessed good practice.

None of them prescribes a mapping depth for every supplier or a particular tool. Each scopes the expectation to the functions or services that matter most, which is the same principle as the method above.

Frameworks at a glance

What each framework expects on supplier dependencies

Each one scopes the expectation to the functions or services that matter most. None prescribes a tool or a fixed mapping depth.

Who each framework applies to, what it expects about supplier dependencies, and what it doesn't require.
FrameworkWho it applies toWhat it expectsWhat it doesn't require
DORA In-scope EU financial entities. A register of all ICT arrangements, including subcontractors that underpin services supporting critical or important functions. Assessment of concentration, substitutability and complex subcontracting chains. Mapping every subcontractor behind every ICT service.
FCA and PRA operational resilience UK firms in scope of SYSC 15A and the PRA's operational resilience rules. Mapping of the people, processes, technology, facilities and information behind each important business service, including what third parties provide. Review after material change and at least annually. A prescribed mapping method. Firms set their own methodology.
NCSC CAF (Principle A4) Organisations assessed against the CAF, including through regulators and government assurance schemes. Knowing the extent of the supply chain behind essential functions, including subcontractors, for a "partially achieved" outcome or better. A specific tool, depth or monitoring frequency.
NIST SP 800-161 Rev. 1 and IR 8276 Guidance, voluntary for most UK organisations. Knowing critical suppliers, understanding the supply chain, collaborating with key suppliers and monitoring throughout the relationship. A tier 2 or tier 3 mapping exercise.
Practical decision rule

Build one dependency map around your critical services and use it as evidence for each framework that applies to you. If you're building separate supplier lists for each regulator, you're doing the same work several times.

DORA

For financial entities in scope of DORA, supplier visibility supports several specific obligations:

  • Article 28(3) requires a register of information covering all contractual arrangements for ICT services provided by ICT third-party service providers.
  • Article 28(4) requires an assessment of relevant risks before entering an arrangement, including whether it could contribute to ICT concentration risk.
  • Article 29 extends this. Entities must consider whether a provider is difficult to substitute, and whether they hold multiple arrangements with the same or closely connected providers. They must also assess whether long or complex subcontracting chains could affect their ability to monitor the functions they’ve contracted out.

The register’s templates, set by Implementing Regulation (EU) 2024/2956, record an ICT service supply chain with each provider’s rank in it. According to EIOPA’s published Q&A, subcontractors are included where the service they provide effectively underpins ICT services supporting a critical or important function.

Two limits are worth stating plainly:

  • DORA applies to in-scope EU financial entities, not to every organisation.
  • A dependency map like the template above supports the register, but it isn’t a compliant register of information in itself.

FCA and PRA operational resilience

UK firms in scope of the FCA’s operational resilience rules must identify and document the people, processes, technology, facilities and information needed to deliver each important business service (SYSC 15A.4).

Where a third party delivers part of that service, the FCA expects the firm to understand enough about what supports the third party’s service to meet the same obligation. The PRA sets the same expectation for dual-regulated firms, mapping resources whether or not a third party provides them.

The FCA rule also requires firms to review their mapping after a material change, and in any event at least annually.

NCSC Cyber Assessment Framework

CAF Principle A4 ties supply chain security to the essential functions an organisation delivers. Its indicators make subcontractor visibility explicit:

CAF Principle A4.a
How the NCSC Cyber Assessment Framework describes subcontractor visibility at each outcome level (paraphrased).
CAF outcomeIndicator on subcontractor visibility
Not achieved Parts of the supply chain for an essential function are subcontracted, and the organisation has little or no visibility of those subcontractors.
Partially achieved The organisation knows the extent of its supply chain, including subcontractors.
Achieved The organisation has a deep understanding of its supply chain, including subcontractors and the wider risks it faces.

The CAF is an assessment framework, not a law. It applies through regulators and government assurance schemes, and it doesn’t specify a mapping method or tool.

NIST

NIST SP 800-161 Rev. 1 is NIST’s guidance on identifying, assessing and mitigating cybersecurity risks throughout the supply chain. It covers criticality analysis and keeping an inventory of suppliers.

NIST IR 8276 sets out key practices for managing cyber supply chain risk, including:

  • knowing and managing critical suppliers
  • understanding the organisation’s supply chain
  • collaborating closely with key suppliers
  • assessing and monitoring suppliers throughout the relationship

Both are US guidance. For most UK organisations they’re a reference point rather than an obligation, and neither prescribes a tier 2 or tier 3 mapping exercise.

‍

How do you improve supply chain visibility without mapping everything?

Improve supply chain visibility by mapping to what’s at stake, not to the size of your supplier list. Start with the services the business must keep running, map their suppliers to tier 2, and go deeper only where impact, uncertainty or a shared provider justifies it. Measure progress by what you can now identify and verify, not by how many suppliers the map holds.

Completeness is the wrong target. A supplier list of several hundred names mapped evenly to tier 2 costs a great deal of effort and still leaves the important questions unanswered, because most of those relationships support nothing the business would miss for a week. A map built around a handful of critical services, with known gaps recorded honestly, can answer the questions that matter in an incident or a board meeting.

Proportionality also has a cost. You’ll be accepting, on the record, that some dependencies remain unknown. That’s defensible when the unknowns sit behind low-impact services and the critical paths have been checked. It’s much harder to defend when the effort has been spread so thinly that no critical service has been mapped properly. Start narrow, prove the method works on one service, then extend it.

Useful measures show whether the work is changing what you can do. These are recommendations, not industry benchmarks:

  • critical services with validated supplier relationships
  • critical engagements with dependency information confirmed within your review period
  • unresolved dependency gaps on critical services, and how long they’ve been open
  • shared providers with an owner and a recorded decision
  • fallbacks tested for independence from the primary
  • time taken, in an exercise, to identify potentially relevant suppliers
  • time taken to obtain verified impact information from them

A tabletop exercise is the quickest way to get the last two. Take a real past incident, such as the CrowdStrike outage, and ask how long it would take today to list the suppliers potentially linked to the affected provider, then how long to confirm which services were actually affected. The gap between those two times shows where to invest next.

The question to bring to the board is simple: what can we now identify, verify or withstand that we couldn’t before?

Forward this

Take this to your Head of Security

Five points you can paste into an email or a meeting note. Pick your sector and the regulatory line changes to match.

Your sector
  1. We can name our critical suppliers, but I'm not confident we know who they depend on to deliver the services we rely on.
  2. If several of them use the same provider, one failure could hit several of our services at once, and we wouldn't see that looking at suppliers one at a time.
  3. If a major provider went down tomorrow, we'd struggle to say quickly which suppliers to contact first or what to tell leadership.
  4. It also feeds directly into what DORA and the FCA's operational resilience rules already ask us to understand about third parties behind our critical services.
  5. It also feeds directly into our CAF assessment, where visibility of subcontractors is part of Principle A4.
  6. It's also one of the first things an auditor or regulator would ask about after a supplier incident.
  7. I'd suggest we start small: run the Supply Chain Risk Exposure Assessment, map one critical service to tier 2, and test what we find in a tabletop exercise.

‍

What to look for in a supply chain visibility platform

A supply chain visibility platform should show which providers sit behind your suppliers, link those relationships to the services you depend on, and keep that picture current without heavy manual effort. Judge it by where its dependency data comes from, what it asks of your suppliers, how it handles change, and what it costs your team to run.

Start by asking whether you need a platform at all. If your critical scope is one or two services and a handful of suppliers, a well-kept spreadsheet built on the template above may be enough. A platform earns its cost when the same work stops scaling. That happens when there are too many critical suppliers to keep current by hand, when the same providers keep appearing across different spreadsheets, or when an incident shows that pulling the picture together takes longer than leadership will wait.

The most important question is where the dependency data comes from, because that decides how far you can rely on it. Broadly, there are three sources:

  • Declared by suppliers. They know their own providers, so these declarations are usually specific, but they depend on suppliers taking part and keeping them up to date.
  • Inferred from external scanning. This can surface technology relationships visible from the internet, but it may miss subcontracting arrangements that leave no external trace.
  • Imported from your own records. Contracts and subprocessor lists are reliable for what they cover, but they’re only as current as the last time someone updated them.

None of these is wrong. The risk lies in a platform that blends them without telling you which is which. Ask any vendor to show, for a single relationship, where it came from, when it was last confirmed and how it would be updated if it changed. If the answer is vague, the map will be too.

Evaluation checklist

Seven questions to ask any supply chain visibility platform

Use these in a demo or an RFP. They test feasibility and evidence quality, not feature count.

Criteria for evaluating a supply chain visibility platform, with the question to ask and the warning sign to watch for.
CriterionQuestion to askWarning sign
Source of dependency data For any one relationship, can you show whether it was declared, inferred or imported, and when it was last confirmed? Every relationship looks equally certain, with no source or date.
Supplier participation What do you ask of my suppliers, what does it cost them, and can they reuse what they share across customers? Coverage depends on suppliers doing significant extra work, with no plan for those who don't.
Service linkage and depth Can I link dependencies to my business services and specific engagements, and go beyond tier 2 where I need to? Relationships are held only at company level, with no link to what they support.
Freshness and change How do updates arrive, and how am I told when a relevant dependency changes? The picture only changes when your team re-runs an assessment.
Concentration view Can I see which providers sit behind several suppliers, and which of my services that affects? Shared providers have to be found by exporting and cross-referencing lists.
Incident workflow When a provider has an incident, how do I find linked suppliers, contact them and track each one's status? Outreach happens outside the platform, so answers end up scattered across inboxes.
Effort and total cost How long until we have a useful map for one critical service, and how much internal time does it take to keep current? The licence is quoted, but the analyst time to run it isn't discussed.
Practical decision rule

Run the demo on one of your own critical services, not the vendor's sample data. If the platform can't show you a useful, sourced picture of that one service, it won't do better across the whole supplier list.

For a UK organisation, add two practical checks. Find out where the platform stores and processes your supplier data, and whether its outputs map cleanly to the frameworks you report against, whether that’s DORA, FCA operational resilience or the CAF. No platform takes on your accountability for supplier risk, and a good one won’t claim to.

For a wider comparison of TPRM tools, see our TPRM software buyer’s guide.

‍

How we approach this at Risk Ledger

Risk Ledger connects organisations and their suppliers on a shared network. Each supplier completes one standardised security profile, shares it with the customers that need it and keeps it updated. Suppliers can connect to their own suppliers in the same way, and those connections let customers see beyond tier 1.

The method in this guide works in a spreadsheet, but the collection behind it doesn’t scale well. Every customer asks the same supplier the same dependency questions. The supplier answers each one separately, in a different format each time. When something changes, the answer sitting in each customer’s spreadsheet doesn’t change with it.

A shared profile reverses that pattern. The supplier maintains its information once. Every connected customer then works from the same current version, and the dependency question gets answered once rather than many times.

What Risk Ledger users can see:
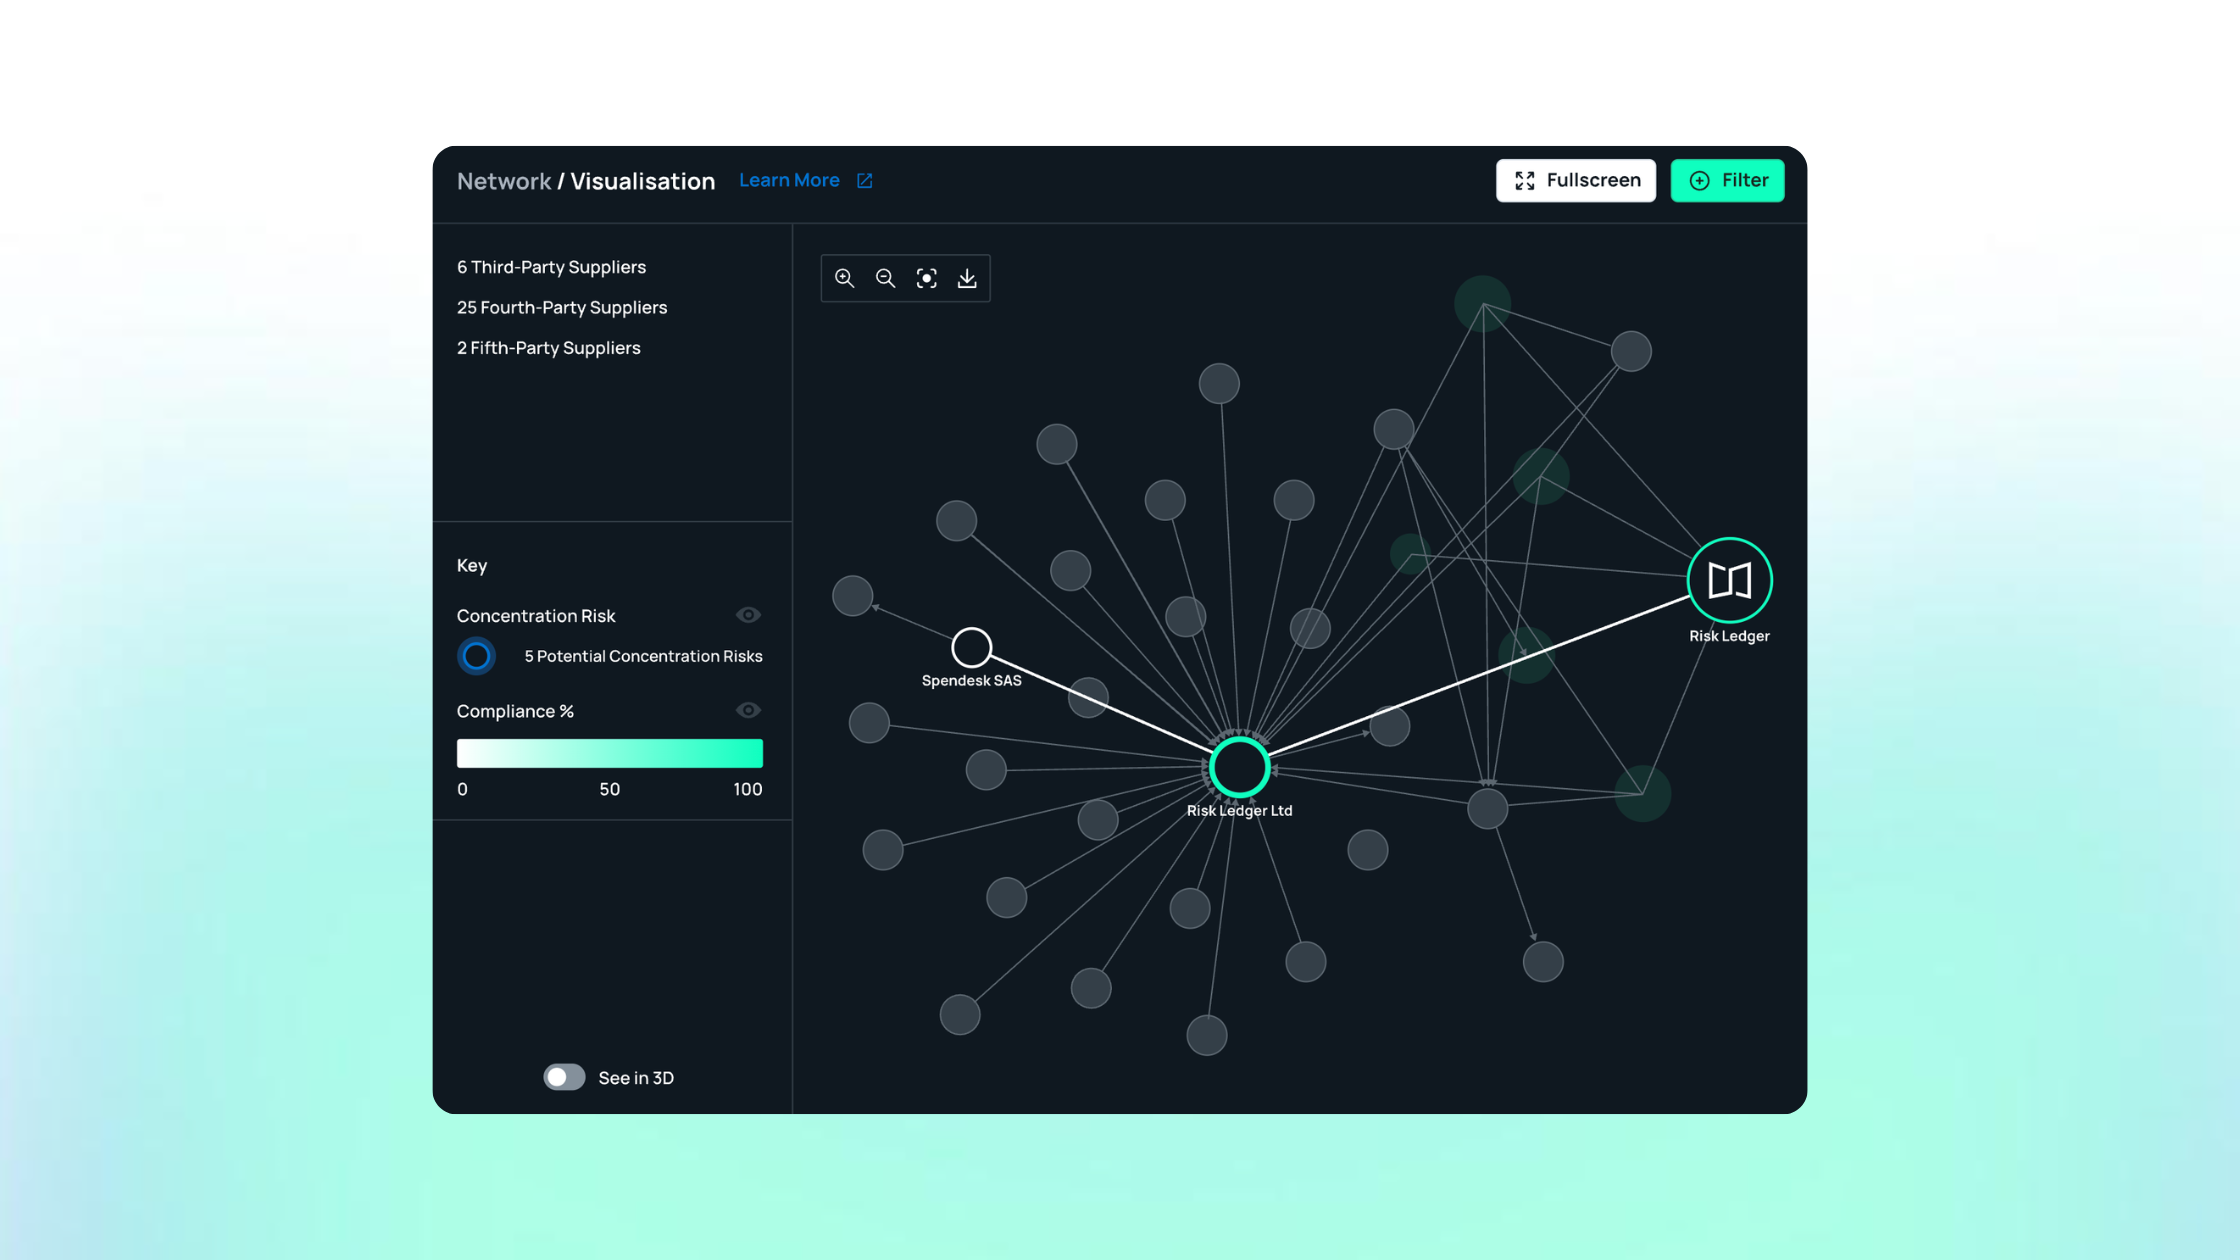
  • A network view of third, fourth and nth parties for suppliers connected on the network.
  • Concentration across the network, showing where one provider sits behind several of your suppliers. You can move from that overview down to the individual suppliers involved.
  • Exposure when a new threat emerges, showing which connected suppliers are linked to an affected organisation, so outreach starts with the right ones.
Risk Ledger Supply Chain Visibility

See where your approach leaves gaps. Run the Supply Chain Risk Exposure Assessment for a directional view of where your current approach to suppliers leaves you exposed. It works from your answers, so it won’t map your actual suppliers. To see your own suppliers’ dependencies on the network, talk to our team.

‍

What the data shows at network scale

Security teams don't just feel this supply chain visibility gap, they name it as the single biggest problem with their current approach. 

In our Every Link Matters 2026 survey of 500 UK cyber security and third-party risk professionals, more respondents pointed to a lack of visibility beyond direct third parties than to any other shortcoming, more than budget, more than resourcing, more than anything else on the list.

Our own network data shows what closing that gap looks like in practice. Across three UK communities on our platform, spanning central government, local authorities and financial services, extending the map from direct suppliers to their nth-party dependencies surfaced roughly three previously unrecorded connections for every direct supplier already known. Most of what's actually out there simply isn't on the register yet.

Most of what's actually out there simply isn't on the register yet.

Network-scale evidence

What the data shows

24.8%

named lack of visibility beyond direct third parties as the single biggest shortcoming in their TPRM approach, the top answer given

2026 UK survey
82.4%

experienced at least one supply chain incident in the past 12 months

2026 UK survey
~2.9x

previously unknown dependencies surfaced for every direct supplier already on record

Risk Ledger network data

How far does visibility actually reach?

Self-reported visibility into supply chain dependencies, 2026 UK survey

  • Full visibility into the entire subcontractor chain for important business functions

  • High visibility into direct subcontractors of critical third parties only

  • Partial visibility into fourth parties

  • No visibility beyond direct critical third parties

‍

What security teams ask next about supply chain visibility

‍

Supply chain visibility FAQs

What is another word for supply chain visibility?

You'll see supplier visibility, nth-party visibility and end-to-end supply chain visibility used for much the same idea. Transparency is often used interchangeably too, and NIST's glossary lists it as a synonym. For security teams, though, transparency usually means what a supplier chooses to disclose, while visibility means what you can see about who your services depend on.

What is end-to-end supply chain visibility?

End-to-end supply chain visibility means understanding the participants and activities across a supply chain, from the earliest sources to the final customer. In cybersecurity, the practical goal is narrower: visibility beyond direct suppliers into the dependencies that support your critical services. It describes a direction of travel, not a promise that every dependency can be found.

Is supplier visibility the same as logistics visibility?

No. Logistics visibility tracks goods, orders and shipments as they move, often through control towers and tracking data. Supplier visibility for security tracks which organisations your services depend on, what data and access they hold, and where several suppliers share a provider. The two use the same words, so check which meaning a tool or guide is using.

What is the difference between tier 2 and tier 3 suppliers?

A tier 2 supplier, or fourth party, is a provider your direct supplier relies on to deliver the service you receive. A tier 3 supplier, or fifth party, is the provider behind that tier 2 supplier. Tier describes a relationship rather than a type of company, so the same provider can be tier 1 for one of your services and tier 2 for another.

How far down the supply chain should you map?

Map tier 2 for the services the business can't afford to lose, then go deeper only where impact, uncertainty or a provider shared across several suppliers justifies it. Mapping every supplier to the same depth takes more effort than most teams have and answers fewer useful questions than a focused map with its gaps recorded.

Can a dependency map tell you whether you were affected by an incident?

Not on its own. A map shows potential exposure: which suppliers and services are linked to the affected provider. Confirming actual impact needs current evidence, such as whether the affected product or version is in use for your service and whether disruption or data exposure has been confirmed. The map tells you who to ask first.

What should you do if a supplier won't disclose its providers?

Record it as unknown rather than leaving it blank, then try alternatives in proportion to how critical the supplier is. Offer a confidential sharing route, ask for a service-level summary, check contracts and published subprocessor lists, and ask about resilience even where names are restricted. A non-response doesn't mean there are no dependencies, and it doesn't prove poor security.

Does AI introduce new supply chain visibility risks?

It can. When an existing supplier adds an AI feature, it may introduce a new provider, new data flows and new behaviour if that provider is unavailable, none of which your original assessment covered. Treat it as a material change: ask who provides the model, what data is sent, what terms apply and whether the feature can be switched off.

What is the difference between supply chain visibility software and a TPRM platform?

A TPRM platform is mainly built to assess individual suppliers: collecting evidence, scoring controls and tracking remediation. Supply chain visibility tooling focuses on the relationships between suppliers, such as who depends on whom and where providers are shared. Some platforms do both. When comparing them, check where dependency data comes from and how current it is, as set out in what to look for in a visibility platform.

‍

Sources

NIST Computer Security Resource Center, Glossary: Visibility
Information Commissioner’s Office,
Contracts and liabilities between controllers and processors
European Union,
Regulation (EU) 2022/2554 on digital operational resilience for the financial sector (DORA)
NHS England,
NHS London statement on Synnovis ransomware cyber attack, 6 June 2024
National Institute of Standards and Technology,
NIST IR 8276: Key Practices in Cyber Supply Chain Risk Management
National Institute of Standards and Technology,
NIST SP 800-161 Rev. 1: Cybersecurity Supply Chain Risk Management Practices for Systems and Organizations
Financial Conduct Authority,
CrowdStrike outage: lessons for operational resilience
National Cyber Security Centre,
Log4j vulnerability: what everyone needs to know
European Insurance and Occupational Pensions Authority,
DORA Q&A 3210: subcontractors in the register of information
Financial Conduct Authority,
FCA Handbook, SYSC 15A.4: Mapping
Prudential Regulation Authority,
SS1/21 Operational resilience: impact tolerances for important business services, Chapter 5: Mapping
National Cyber Security Centre,
Cyber Assessment Framework, Principle A4: Supply chain
Blog

Download for free

Pattern Trapezoid Mesh

Get the security manager's briefing

Monthly research, case studies and practical guides you won't find anywhere else.

Join thousands of security managers turning their TPRM programmes into success stories.